Connected. Deliberately.
Connect approved MCP clients and upstream systems through Durin’s identity, consent, policy, and production trust boundary.
Build your connection plan.
 GitHub
 Jira
 Slack
 Notion
 Linear
 Google Drive
 Gmail
 Sentry
 PostHog
and more…
These are connection setup paths. Consent, discovery, activation, and verification remain prerequisites before a production connection is used.
Keep the client path and provider path separate.
Each integration has two trust relationships: the employee or client to the Durin gateway, and Durin to the upstream system. Their identities, grants, scopes, and trust states remain distinct.
MCP-compatible clients
Configure a supported client to use the gateway. The MCP protocol path covers current behavior and an explicitly tested legacy initialize path; hosted OAuth setup must be verified.
Upstream systems
Provider setup guides cover GitHub, Atlassian, Slack, Google Workspace, Linear, Notion, Sentry, PostHog and Custom MCP. Each guide identifies its available setup path and prerequisites; consent, discovery and activation remain provider-dependent.
A safe place to begin
Begin with policy, approvals, audit, and uncertain-outcome review before connecting production provider access through explicit trust checks.
Your internal MCP belongs in the review flow, too.
Request a custom server with a URL and intended use. Administrators approve setup; the requester is notified when the connection becomes available.
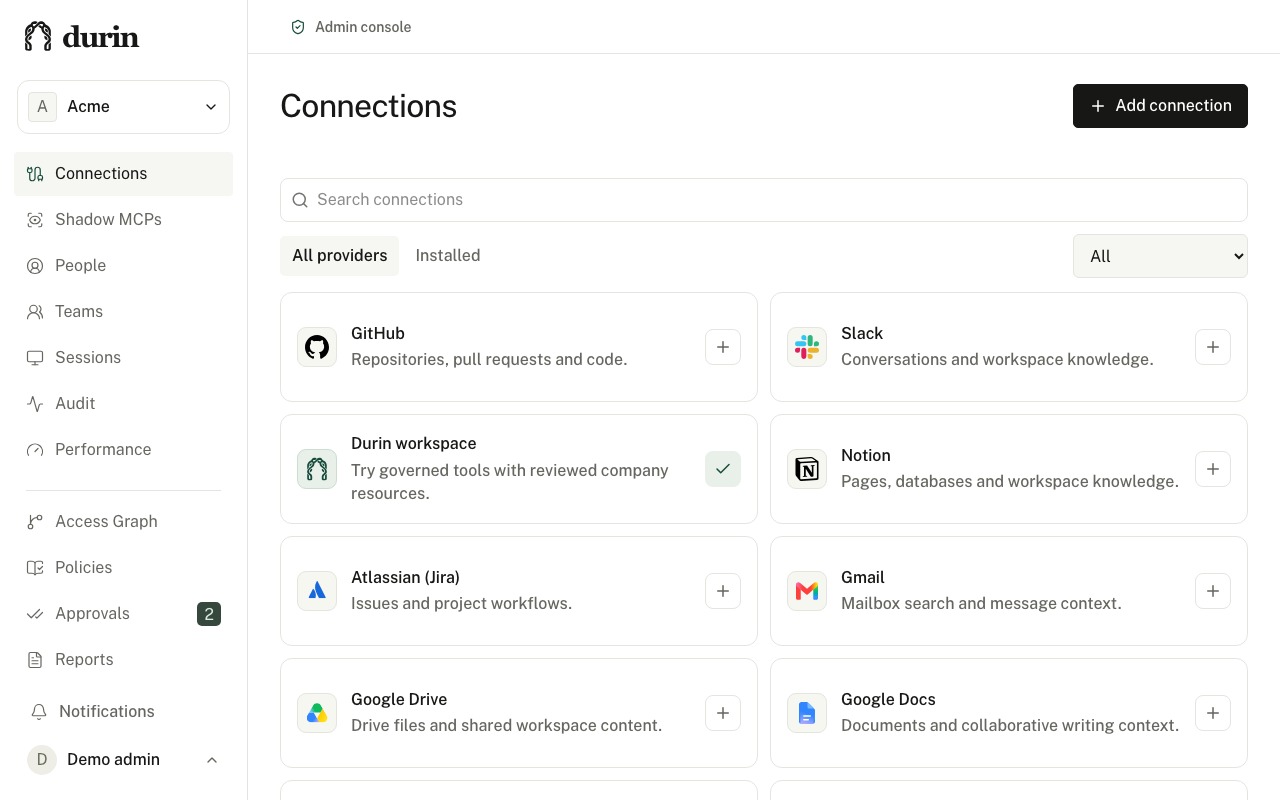
Plan each connection boundary.
Create an account to manage connection setup, client paths, and the provider checks required before activation.
Create an account