Decide before agents act.
Review Durin’s MCP security controls for AI agents: identity checks, access policies, independent approvals, and audit records for routed requests.

Control the action before it runs.
- Control actions
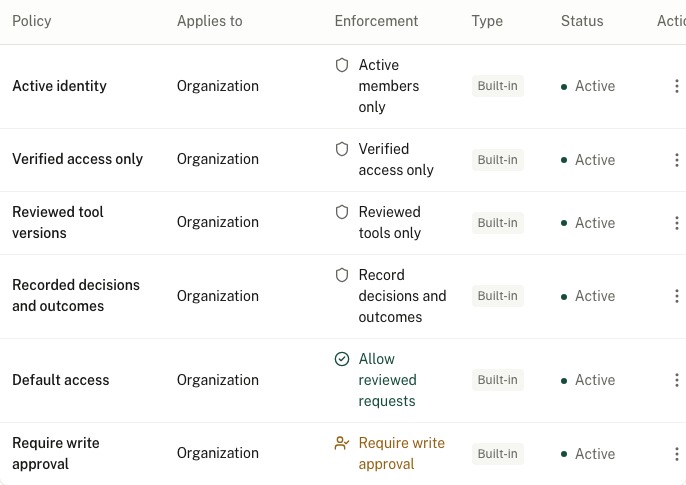
Reviewed requests can run after the required checks. Choose default deny, require approval for changes, or block changes.
- Require a reviewer
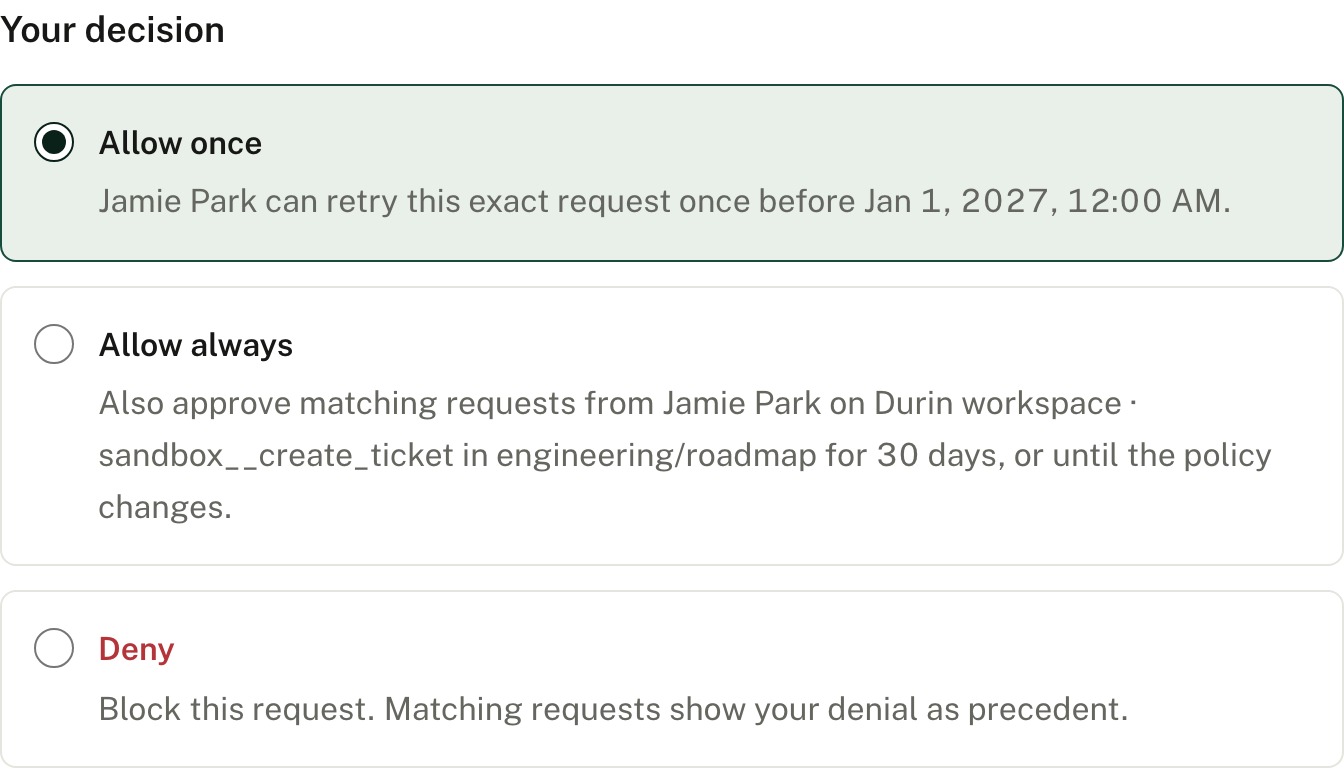
The requester cannot approve their own action. Approval is tied to the exact request, expires and can be used once.
- Revoke access
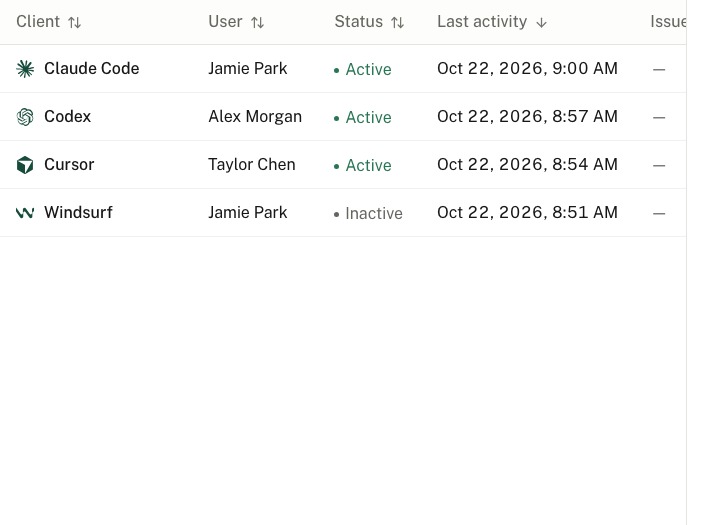
Revoke a session, member or connection. Current authority is checked again before a governed request runs.
- Inspect the record
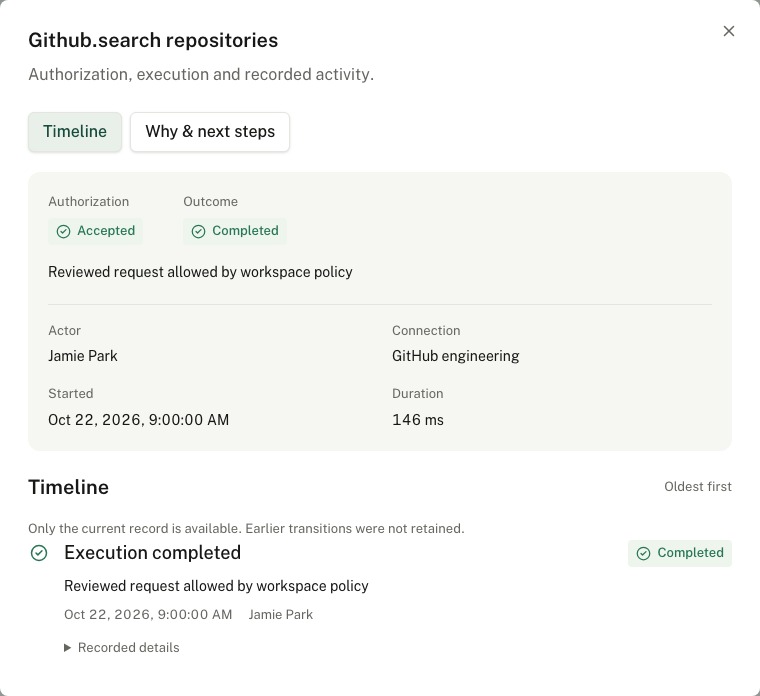
Audit intent is recorded before execution. A permitted action and a confirmed result are recorded as separate facts.


Coverage starts with the route.
Through the Durin gateway
- Current identity, organization, and connection checks.
- Default allow, operator-controlled denial, and exact approvals where required.
- Audit intent and a recorded execution outcome.
Requires separate controls
- Direct API calls, browser actions, shell commands, and clients that bypass Durin.
- Upstream permissions and how an external model provider handles returned data.
- Customer network restrictions and deployment-specific coverage tests.
Know what is protected.
- Identity and access
- Current membership and authority are checked before a governed request runs. Provider permissions still apply.
- Connection credentials
- Connection credentials are encrypted and scoped to their intended use. A Durin approval cannot expand provider permissions.
- Audit data
- Governance metadata is recorded by default. Administrators control optional redacted message capture.
- Models and operators
- Durin does not train AI models. Your agent’s model provider can receive the tool results returned to that agent.
Find gaps in your AI setup.
Answer ten questions or check a config. See your grade first.